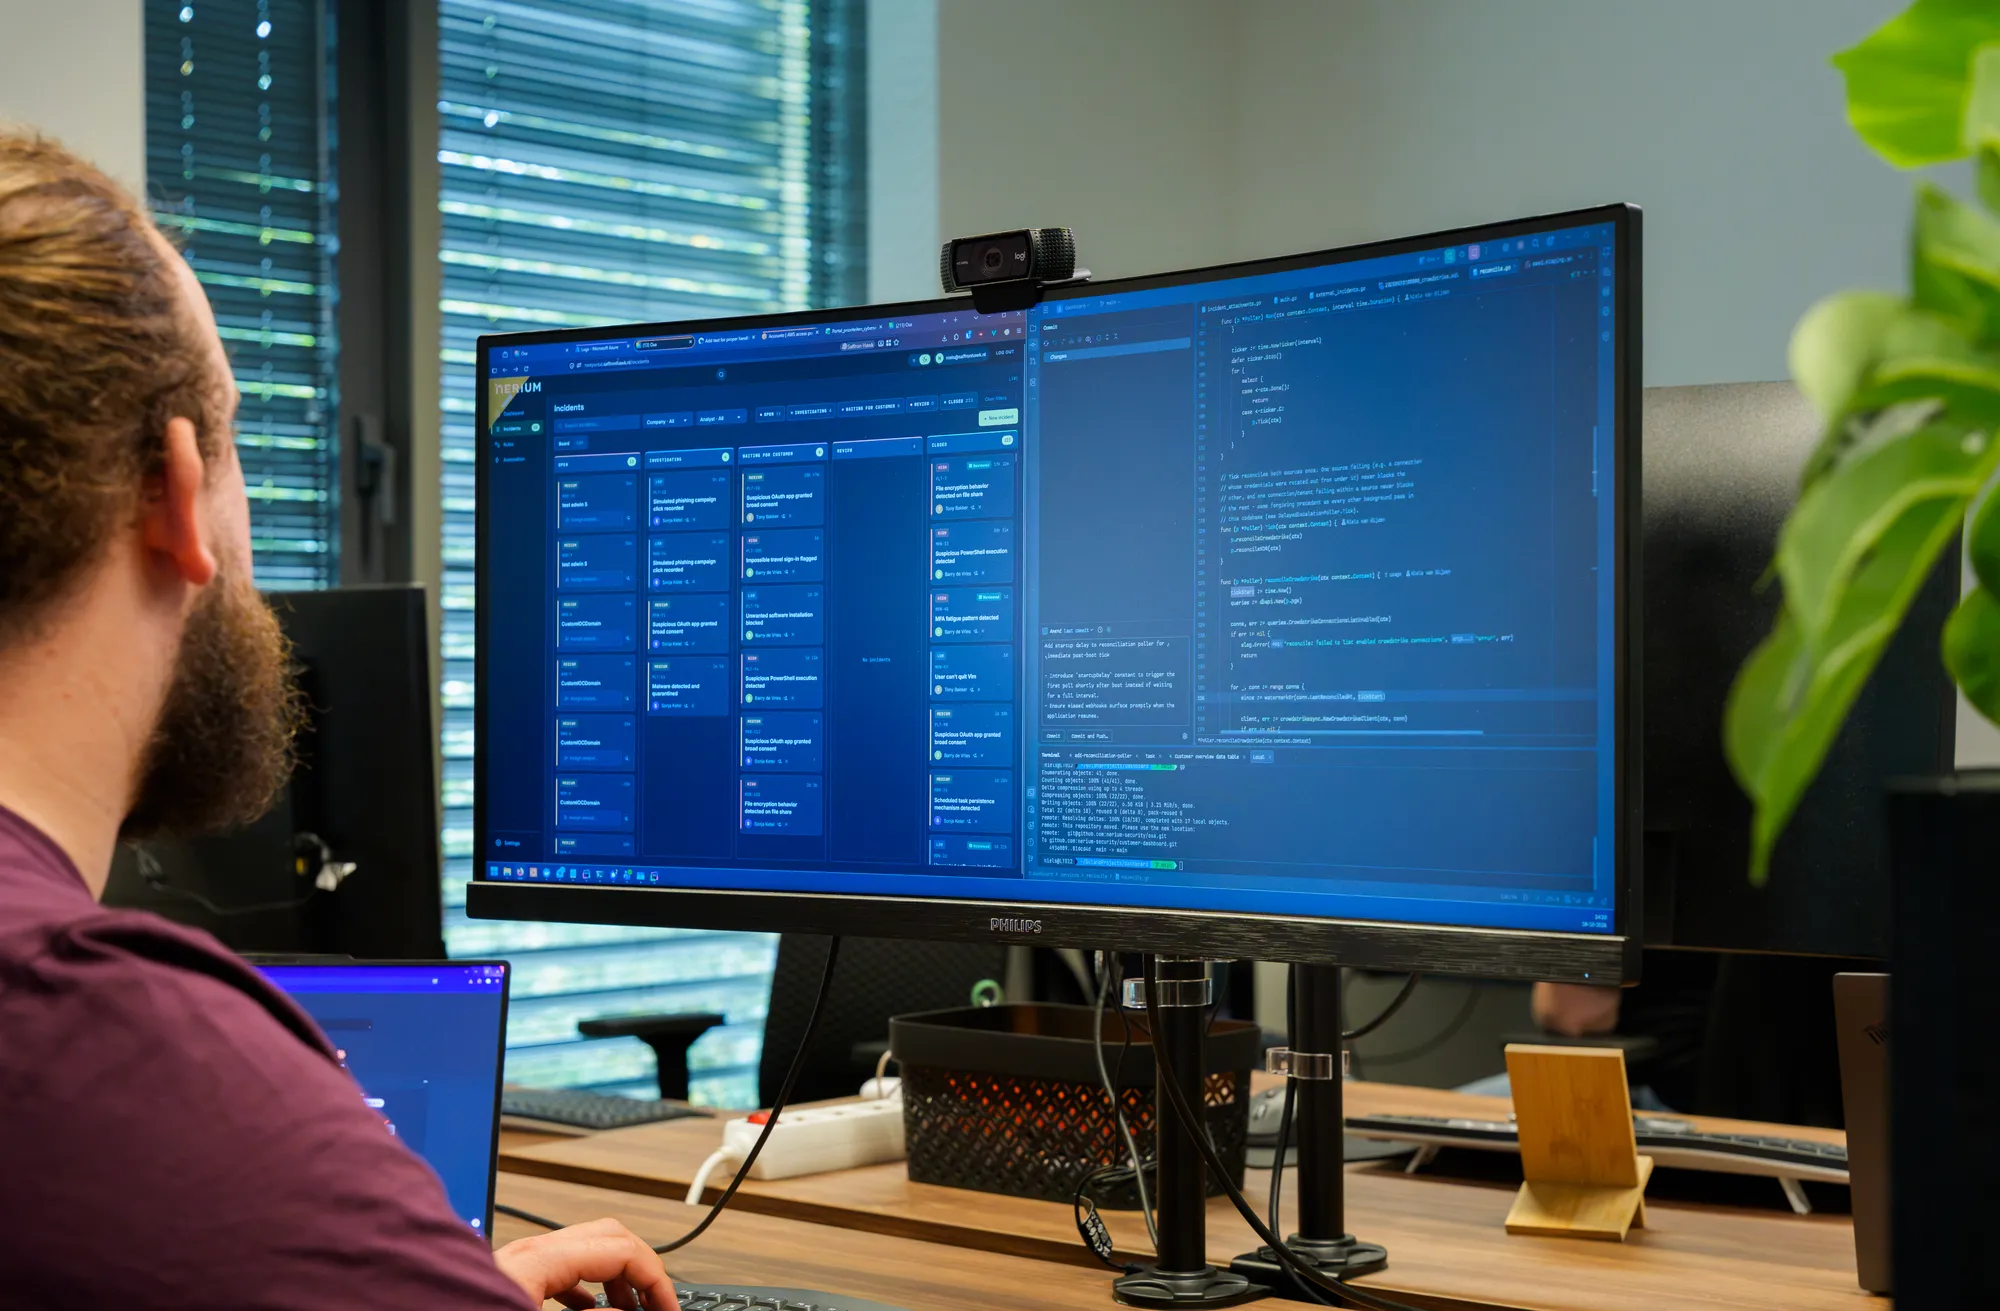
Standard detection doesn’t catch everything. We go one step further.
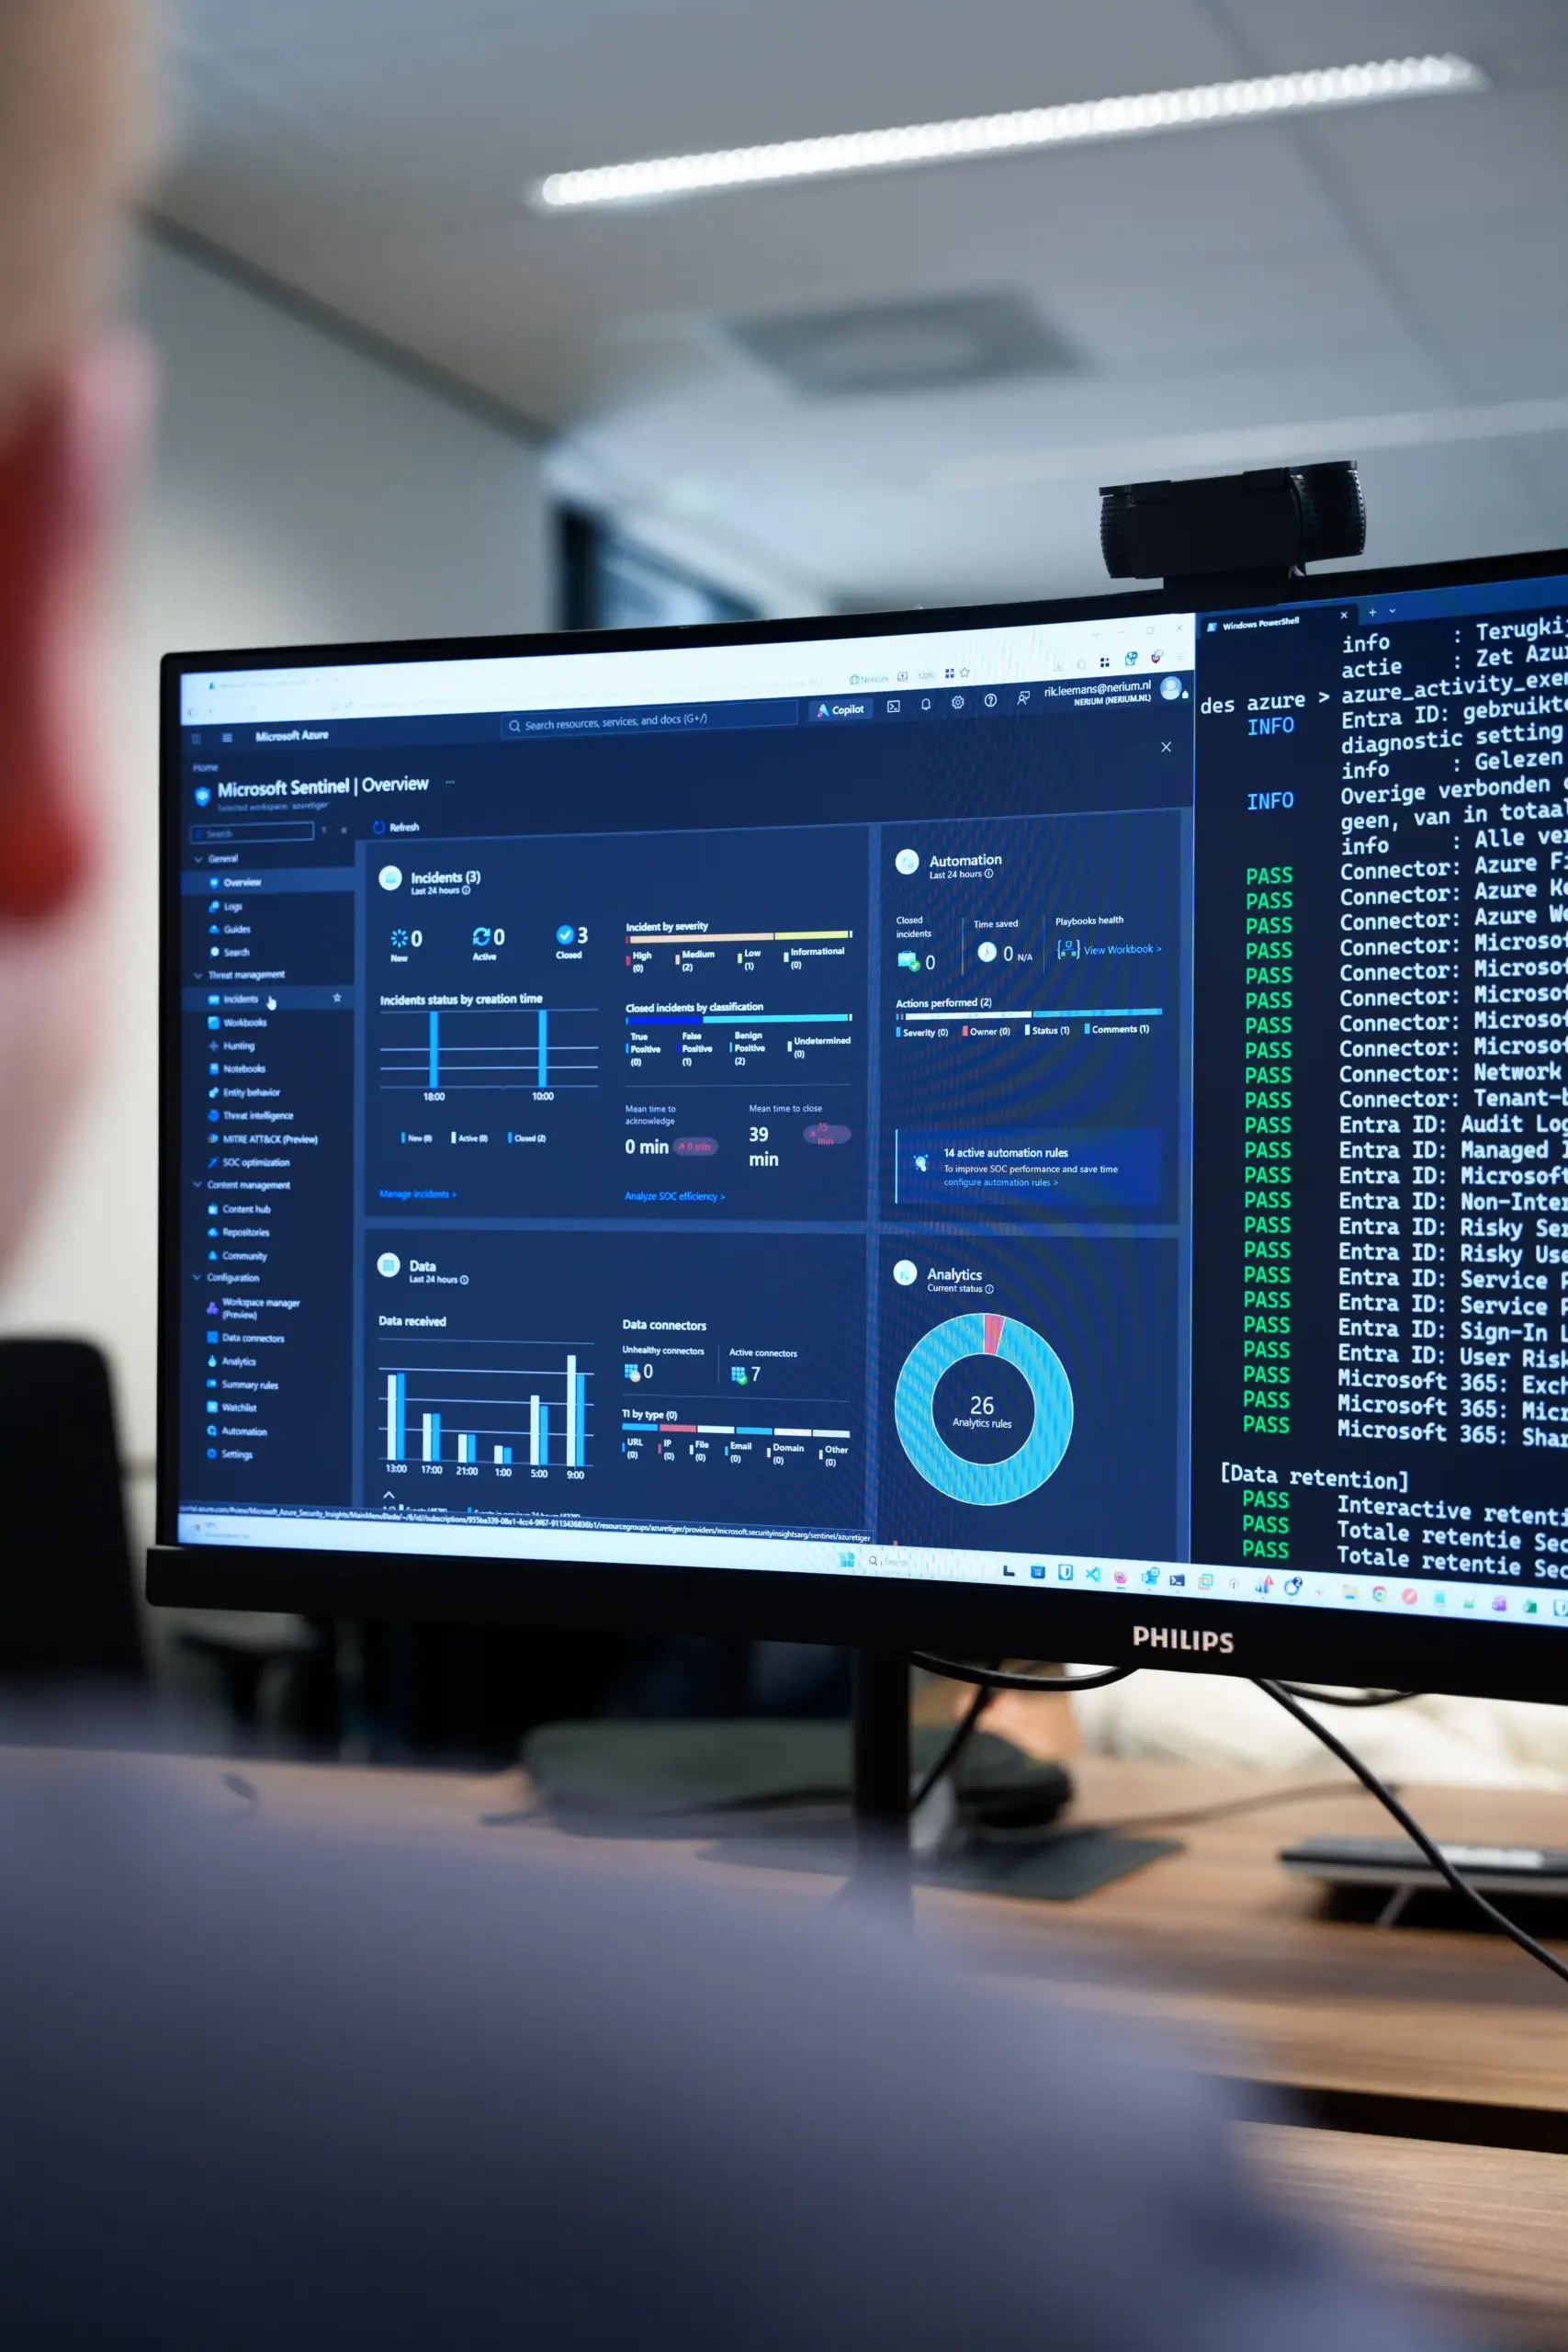
Security solutions such as Microsoft Defender and CrowdStrike form an important foundation for cyber detection, but they are not familiar with your specific IT environment. As a result, suspicious activities may go undetected, such as the misuse of administrative privileges, compromised accounts or attacks via bespoke applications and external links.
Nerium addresses these blind spots with its own detection rules. These are based on realistic attack techniques and tailored to the risks and business processes that are important to your organisation.