Managed Detection
& Response (MDR). Customized
detection. 24/7 protection.

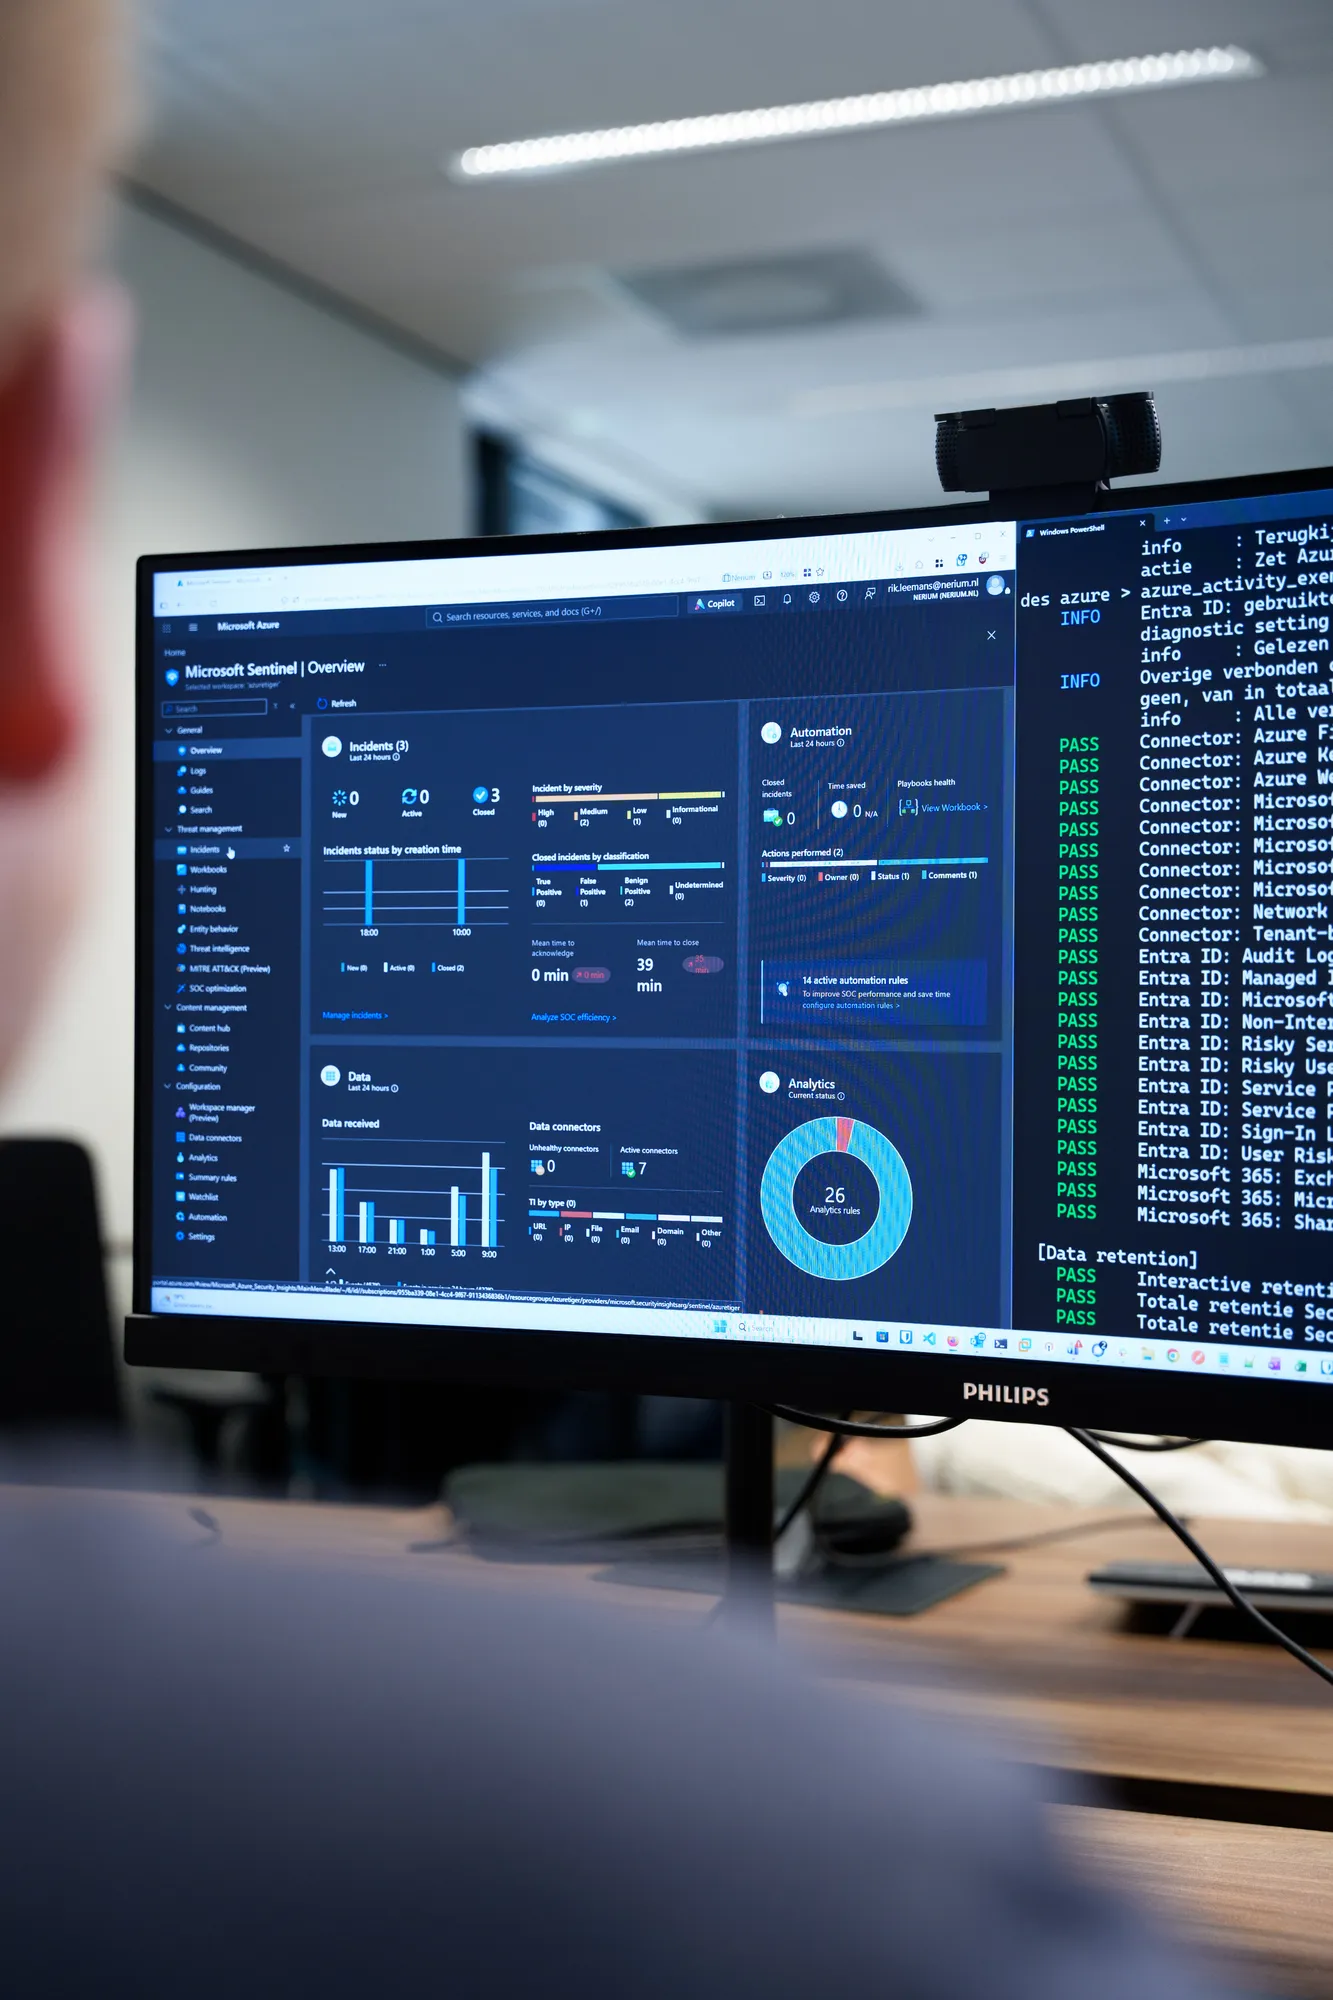
Cyber threats don’t stop after business hours. With Managed Detection & Response (MDR), Nerium monitors your IT environment 24/7, detects suspicious activity, and takes immediate action when necessary. One Dutch team, from initial detection to full incident resolution.

  • Customized Multi-Layered Detection
  • Immediate response
  • No vendor lock-in
Managed Detection& Response (MDR). Customizeddetection. 24/7 protection.

“Not a traditional supplier, but a committed security partner based in the Eindhoven region. Communication lines are short and they know our organisation.”

“Whether it’s a minor report or a serious incident, we know that Nerium is there for us 24/7.”

“With Nerium, we’ve got our digital security well organised, without having to do everything ourselves. It’s exactly the support we need.”

“Thanks to Nerium’s specialist knowledge, we can continue to focus on providing high-quality and safe care for our clients.”

“With Nerium as our partner, I sleep much more soundly. Their expertise and 24/7 protection give us peace of mind.”

“Greater control over our digital security, specialist knowledge and a swift response. That gives us confidence and peace of mind.”

“Specialist knowledge is not a luxury for our sector, but a necessity. Nerium’s targeted approach is convincing.”

More than just security monitoring. Targeted protection.

More than just security monitoring. Targeted protection.

A cyberattack can escalate at lightning speed. Without continuous monitoring, the right detection rules, and immediate follow-up, threats may go unnoticed. But how do you ensure effective security without having to set up a full-fledged Security Operations Center (SOC) yourself?


With Nerium’s MDR, you gain the expertise and capacity of a specialized security team. Our analysts investigate reports, develop detection rules, conduct threat hunts, and intervene immediately when necessary. We also responsibly utilize (agent-based) AI and smart automation where appropriate to accelerate analyses and investigate threats more efficiently. No endless stream of unassessed alerts—just concrete conclusions, clear recommendations, and targeted actions.
Effective detection starts with understanding

No two IT environments or threat landscapes are alike. That’s why we don’t start with the technology, but with the risks that are truly important to your organization. Which systems are critical? How can attackers gain access to them? And what information is needed to identify threats in a timely manner?

Logging Strategy

We determine which log sources are needed to detect and investigate relevant threats.

Threat Modeling

We identify critical processes, vulnerabilities, and realistic attack scenarios.

Detection Engineering

We develop and manage targeted detection rules using Detection-as-Code.

From Initial Detection to Immediate Response

Our specialists monitor your IT environment 24/7 from a single Security Operations Center in the Netherlands. As soon as a potential threat is detected, we investigate the alert and take action in accordance with predefined procedures.

01. Continuous monitoring

We monitor security alerts, log sources, and the operation of the monitoring system itself. This ensures that suspicious activities and blind spots remain visible.

02. Research and Evaluation

Our analysts investigate suspicious activities within the context of your organization and determine whether there is an actual threat.

03. Take immediate action

If a threat is confirmed, we take immediate action within the agreed-upon mandate, such as isolating a device or blocking an account.

04. Restore and Improve

We oversee the recovery process, evaluate the incident, and, where necessary, improve the detection rules to identify future attacks more quickly.

One Dutch team, available 24/7

Senior analysts and incident responders work together under one roof. From detection to large-scale incidents, without involving external parties.

No vendor lock-in

Our MDR services run in your own tenant. Data, configurations, and customer-specific detections remain the property of your organization, even after the partnership ends.

Detection solutions tailored to your risks

With our own multi-layered detection rules, threat intelligence, and
Detection-as-Code, we can also identify threats that standard security solutions might miss.

Transparent and verifiable

Through our proprietary portal, you’ll have continuous insight into incidents, trends, and areas for improvement. With clear reports and regular meetings, we’ll work together to maintain control over security.

15 min. from detection to isolation

15 min. from detection to isolation

During a red team exercise, our own detection rules identified an attack, and the affected workstations were isolated within 15 minutes.

Real-world example; no guaranteed response time.

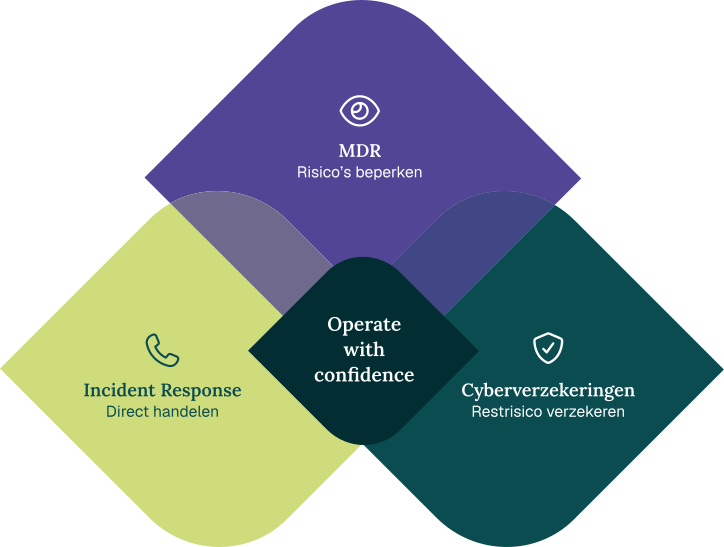
Three core services. One targeted approach.

Three core services. One targeted approach.

With MDR, Nerium lays the foundation for an integrated approach to cybersecurity. We understand your IT environment, monitor security, and respond immediately to threats. Thanks to the included Incident Response Retainer, arrangements for rapid support in the event of major incidents are established in advance. In addition, we help you insure against the remaining cyber risk with targeted cyber insurance.

Proven when it counts

From complex cyberattacks to day-to-day security improvements, Nerium helps organizations across various sectors identify threats in a timely manner, quickly contain incidents, and systematically strengthen their cyber resilience.

Cta image

24/7 protection against cyber threats?

Discover how Nerium helps your organization detect threats in a timely manner and stop them effectively. Our specialists assess what your organization truly needs.

Request a no-obligation consultation