Cybersecurity Compliance. Not just complying, but actually protecting.

The Cybersecurity Act (NIS2), DORA, and security standards set high requirements for digital resilience. Nerium helps you effectively implement cybersecurity measures through 24/7 monitoring, targeted detection, incident response, and insight into your security.

  • Technical Security Measures
  • 24/7 monitoring
  • Insights via Oxa
Cybersecurity Compliance. Not just complying, but actually protecting.

“Geen traditionele leverancier, maar een betrokken securitypartner uit de regio Eindhoven. De lijnen zijn kort en ze kennen onze organisatie.”

“Whether it’s a minor report or a serious incident, we know that Nerium is there for us 24/7.”

“With Nerium, we’ve got our digital security well organised, without having to do everything ourselves. It’s exactly the support we need.”

“Thanks to Nerium’s specialist knowledge, we can continue to focus on providing high-quality and safe care for our clients.”

“With Nerium as our partner, I sleep much more soundly. Their expertise and 24/7 protection give us peace of mind.”

“Greater control over our digital security, specialist knowledge and prompt follow-up. That gives us confidence and peace of mind.”

“Specialist knowledge is not a luxury for our sector, but a necessity. Nerium’s targeted approach is convincing.”

Cybersecurity compliance requires more than just policies.

Cybersecurity compliance requires more than just policies.

Laws, regulations, and security standards require organizations to manage their cyber risks. This means not only establishing policies and procedures, but also ensuring that you can identify threats, handle incidents, and provide transparency into the measures taken.


Nerium assists with the operational implementation of cybersecurity. Through our services, we strengthen your organization’s security and provide information that can help demonstrate compliance with relevant requirements.
What laws and standards are relevant?

Depending on your industry and organization, various legal requirements and security standards may apply. Nerium supports the technical and operational security measures that may be relevant in this regard.

Cybersecurity Act (NIS2)

The Dutch Cybersecurity Act translates the European NIS 2 Directive into obligations for essential and important organizations. These include risk management, incident response, and the reporting of significant cyber incidents.

DORA

The Digital Operational Resilience Act sets requirements for the digital resilience of financial institutions. Monitoring, detection, and effective incident response can help ensure compliance with relevant IT security obligations.

ISO 27001 and BIO2

ISO 27001 and the Government Information Security Baseline (BIO2) provide frameworks for information security. Nerium provides support in the form of operational security measures and guidance on their implementation.

From security requirements to concrete measures.

Nerium helps organizations effectively implement cybersecurity measures—not just through advice or reports, but through operational security and specialized support.

01. 24/7 security monitoring

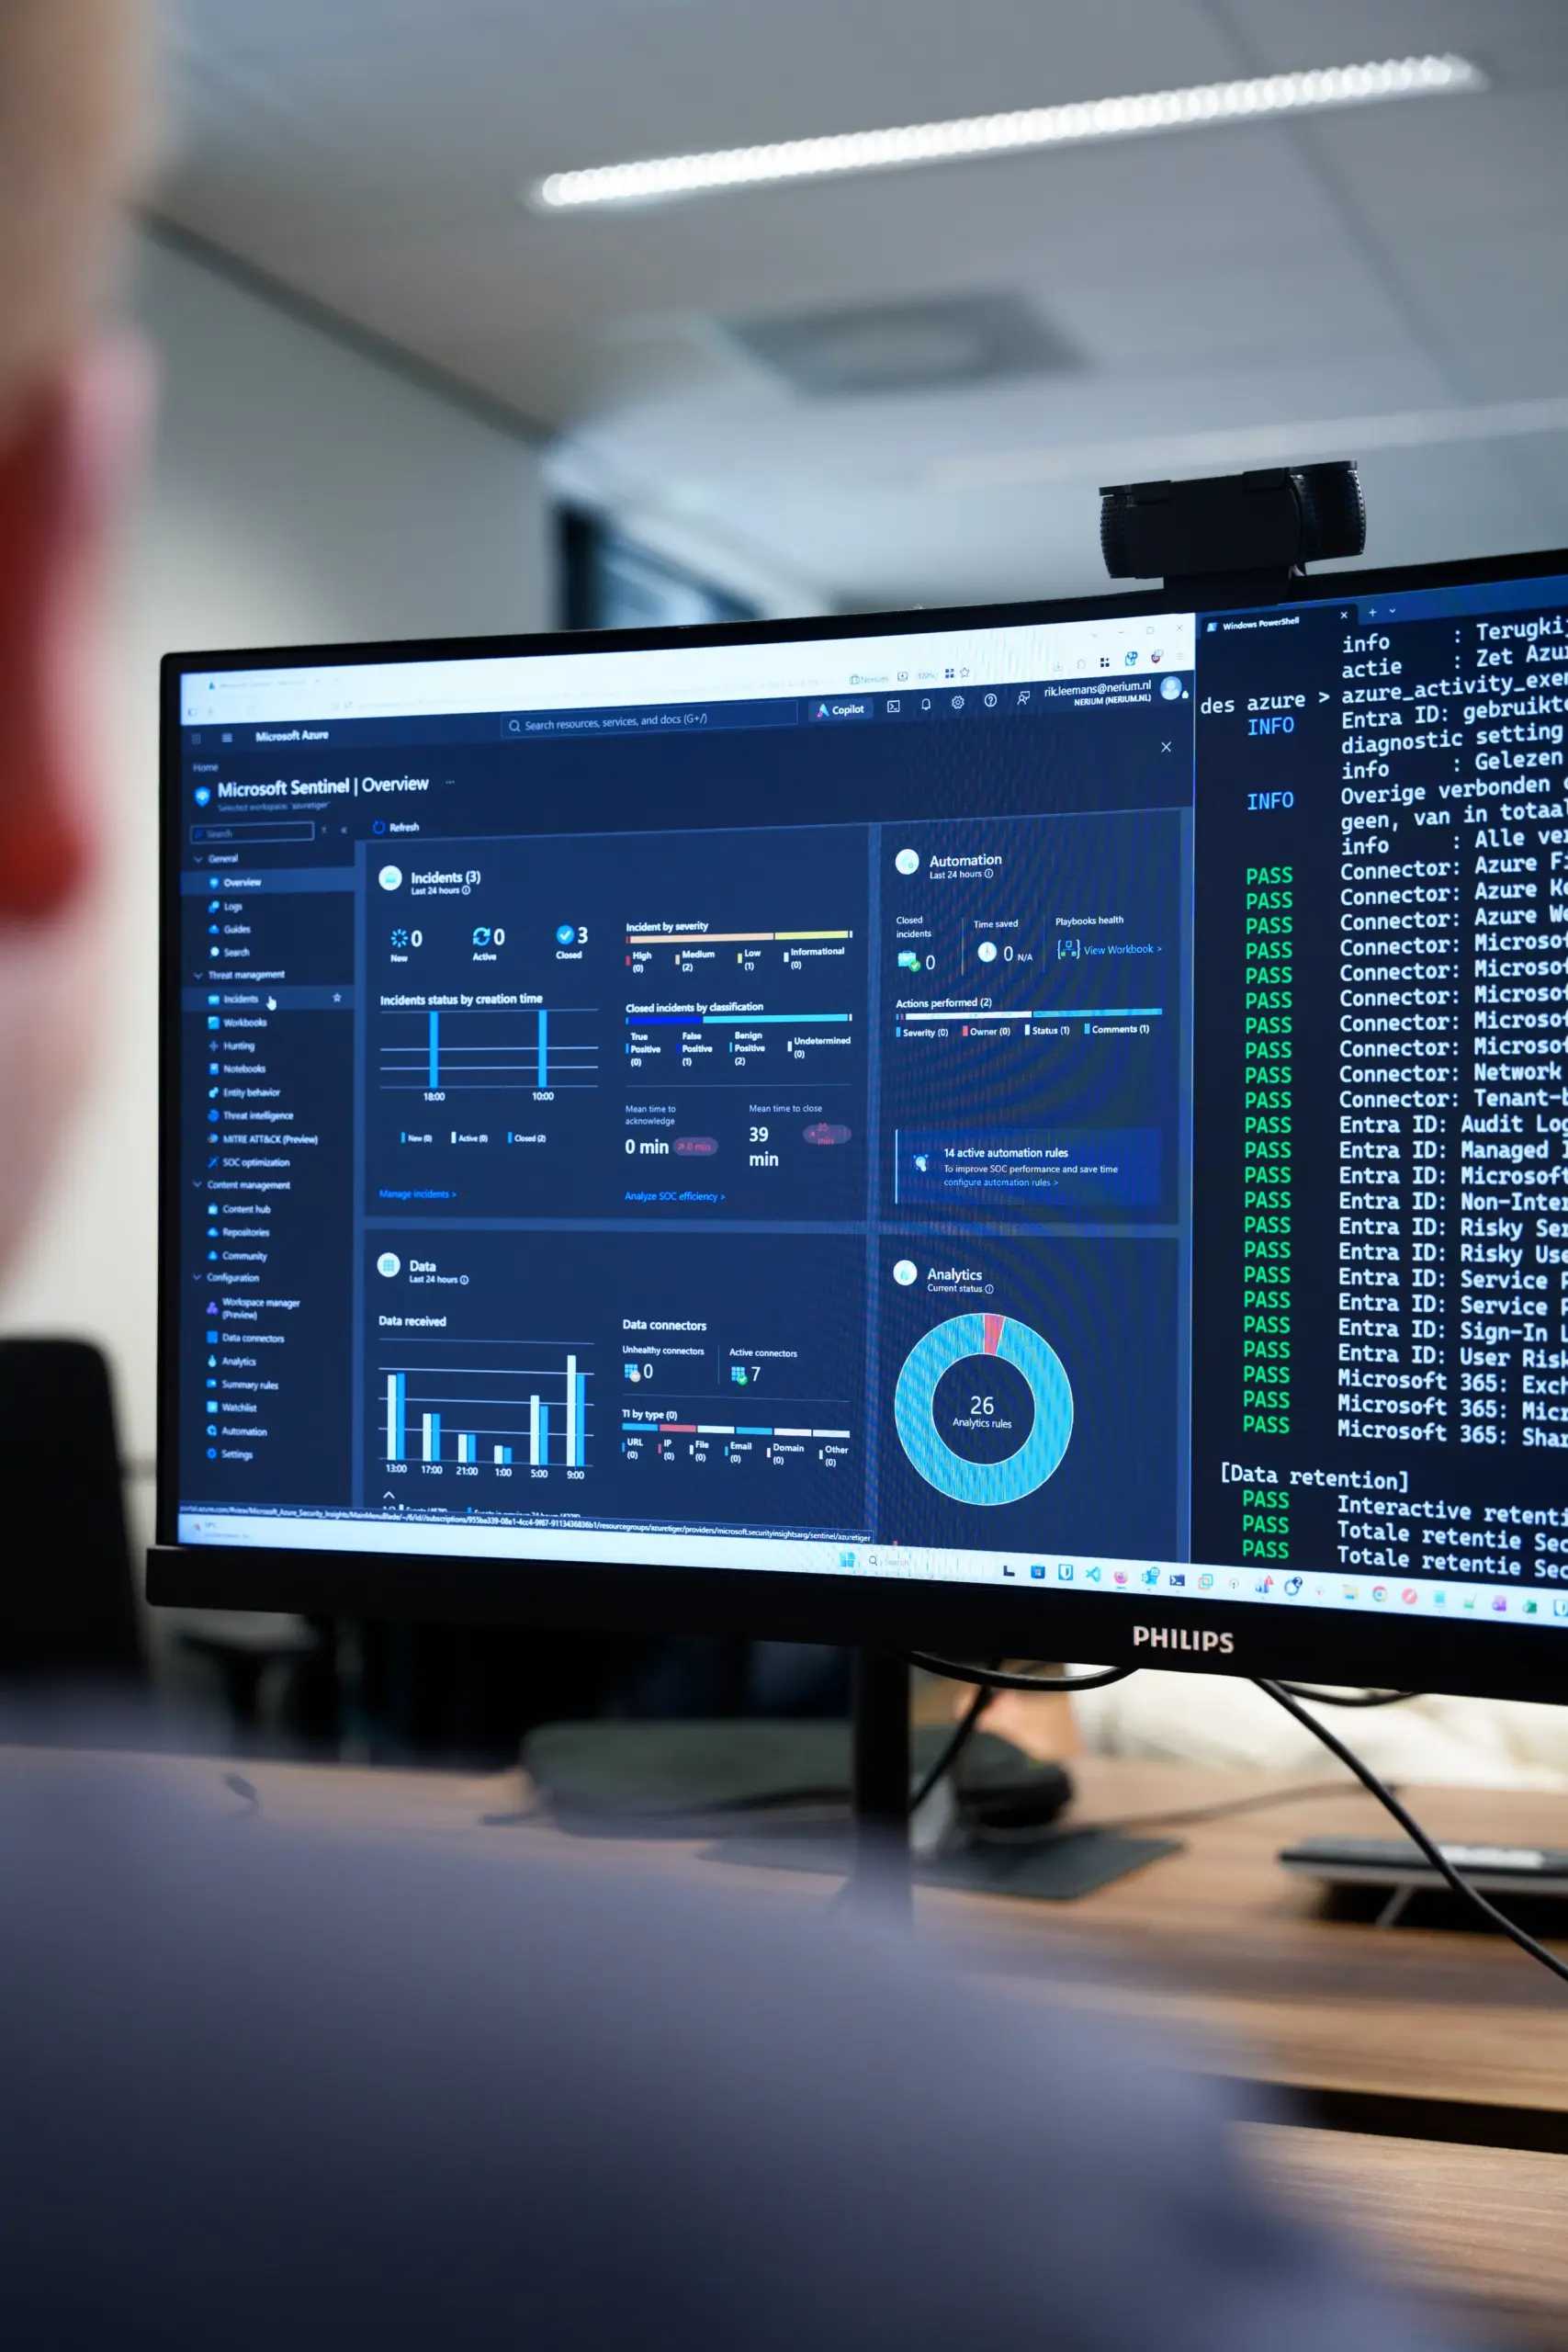
With Managed Detection & Response (MDR), we monitor your IT environment and identify suspicious activity. This enables us to support the continuous detection and response to cyber threats.

02. Detection and Targeted Response

We develop detection rules tailored to your risks and systems. When threats arise, our specialists take action within pre-agreed mandates.

03. Incident Response and Recovery

In the event of cyber incidents, we provide support in the form of investigation, crisis coordination, mitigating the attack, and recovery. We also assist by providing relevant information for incident documentation.

04. Insight and Rationale

We provide insight into the security measures we have implemented and the effectiveness of our detections. This information helps your organization conduct internal audits and demonstrate compliance with relevant requirements.
Insight into your organization’s security.

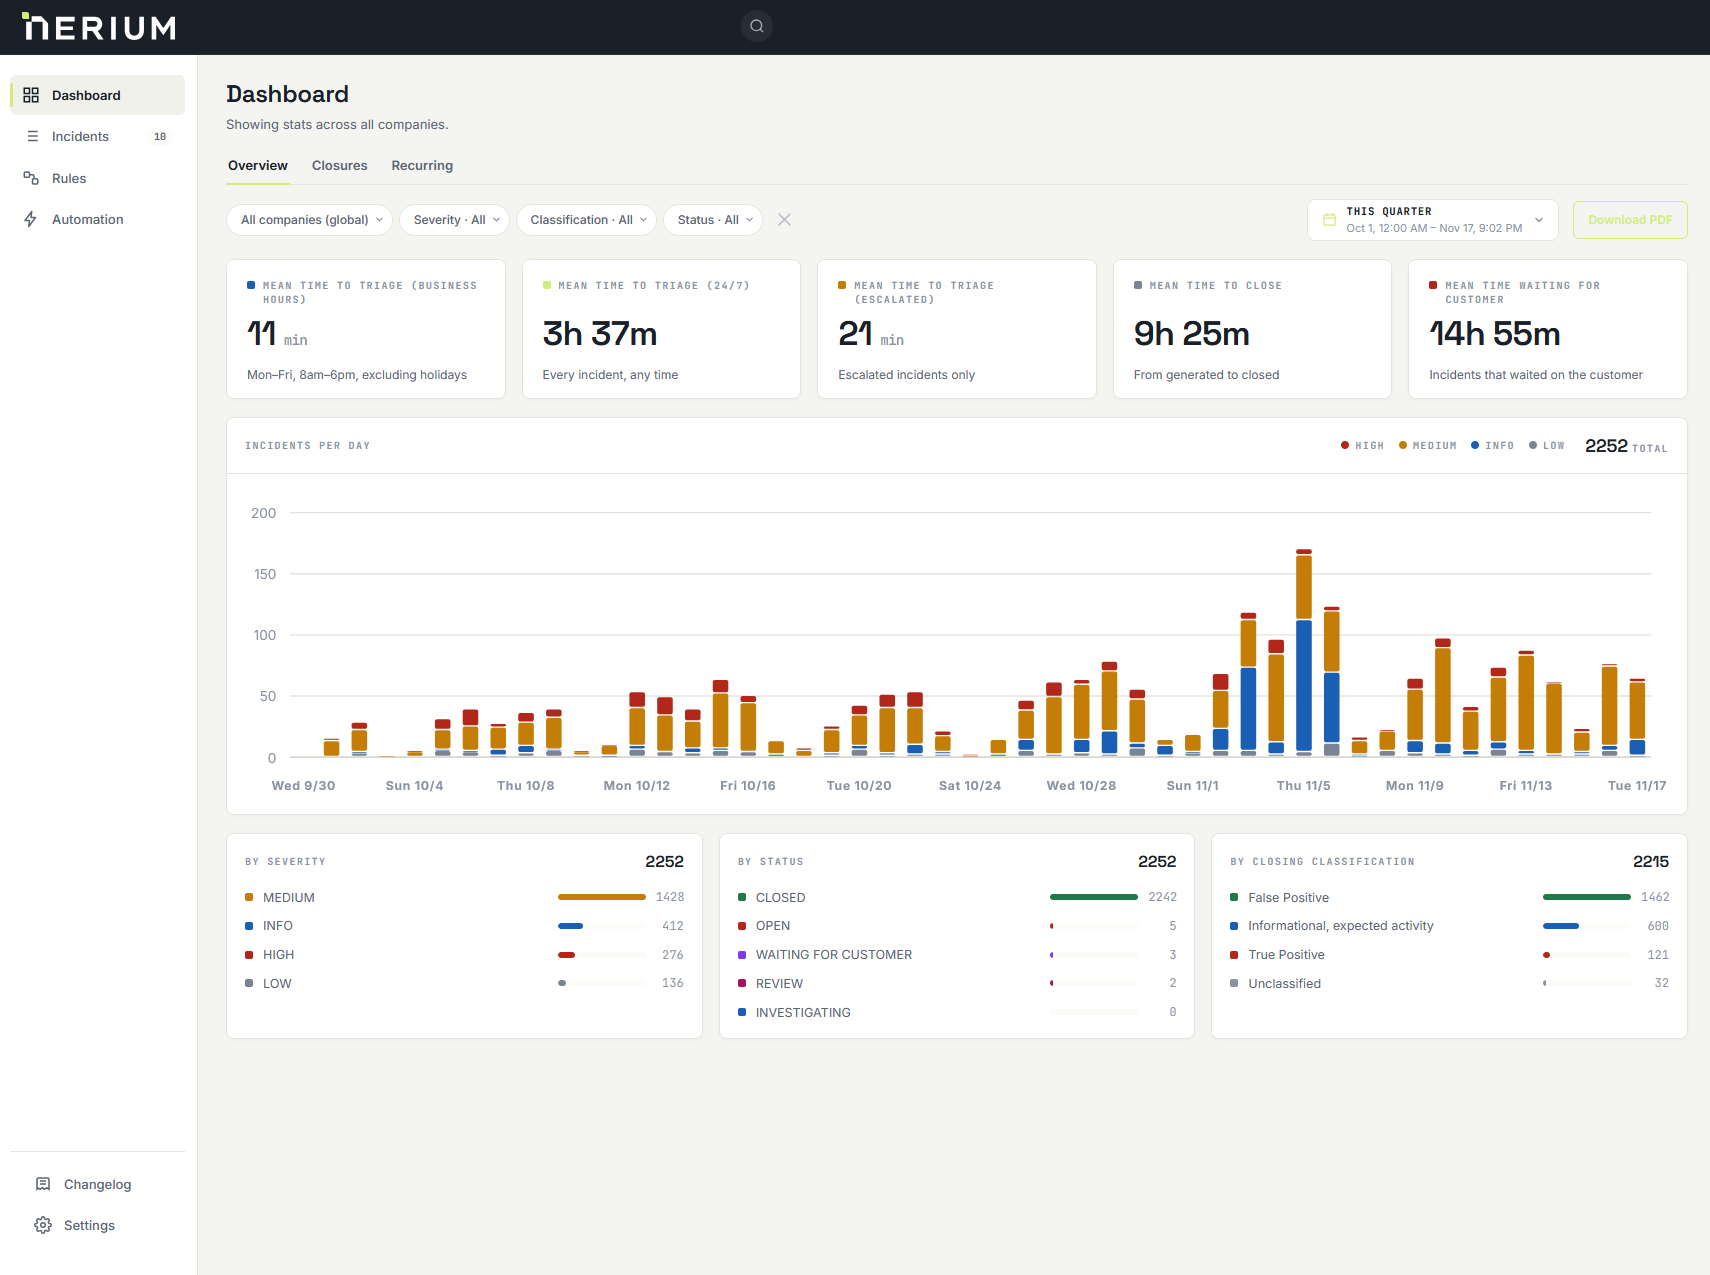
Cybersecurity measures must not only be implemented but also made transparent. Through Oxa, Nerium’s proprietary platform, you gain visibility into active detections, their coverage, and performance.


This information helps your IT and security teams evaluate security, track improvements, and provide relevant supporting documentation for internal audits and compliance processes.

Insight into your organization's security.
Not just a checkmark, but real protection.

Not just a checkmark, but real protection.

With Managed Detection & Response (MDR) and Incident Response, Nerium helps organizations implement relevant security measures. Specialized services such as External Attack Surface Management, Threat Modeling, and Detection Engineering enhance understanding of cyber risks and the effectiveness of detection.


With our cyber insurance, we also help mitigate the financial consequences of cyber incidents. Together, our services strengthen your organization’s digital resilience and support the implementation and justification of relevant security measures.

Trust that proves itself in practice.

Discover how we help organizations across a wide range of industries manage cyber risks and strengthen their digital resilience.

Cta image

From Obligation to Effective Protection?

Discover how Nerium helps your organization implement and provide insight into relevant security measures. Together, we’ll determine what your organization truly needs.

Request a no-obligation consultation