Hybrid SOC. Your security team. Nerium as an extension.

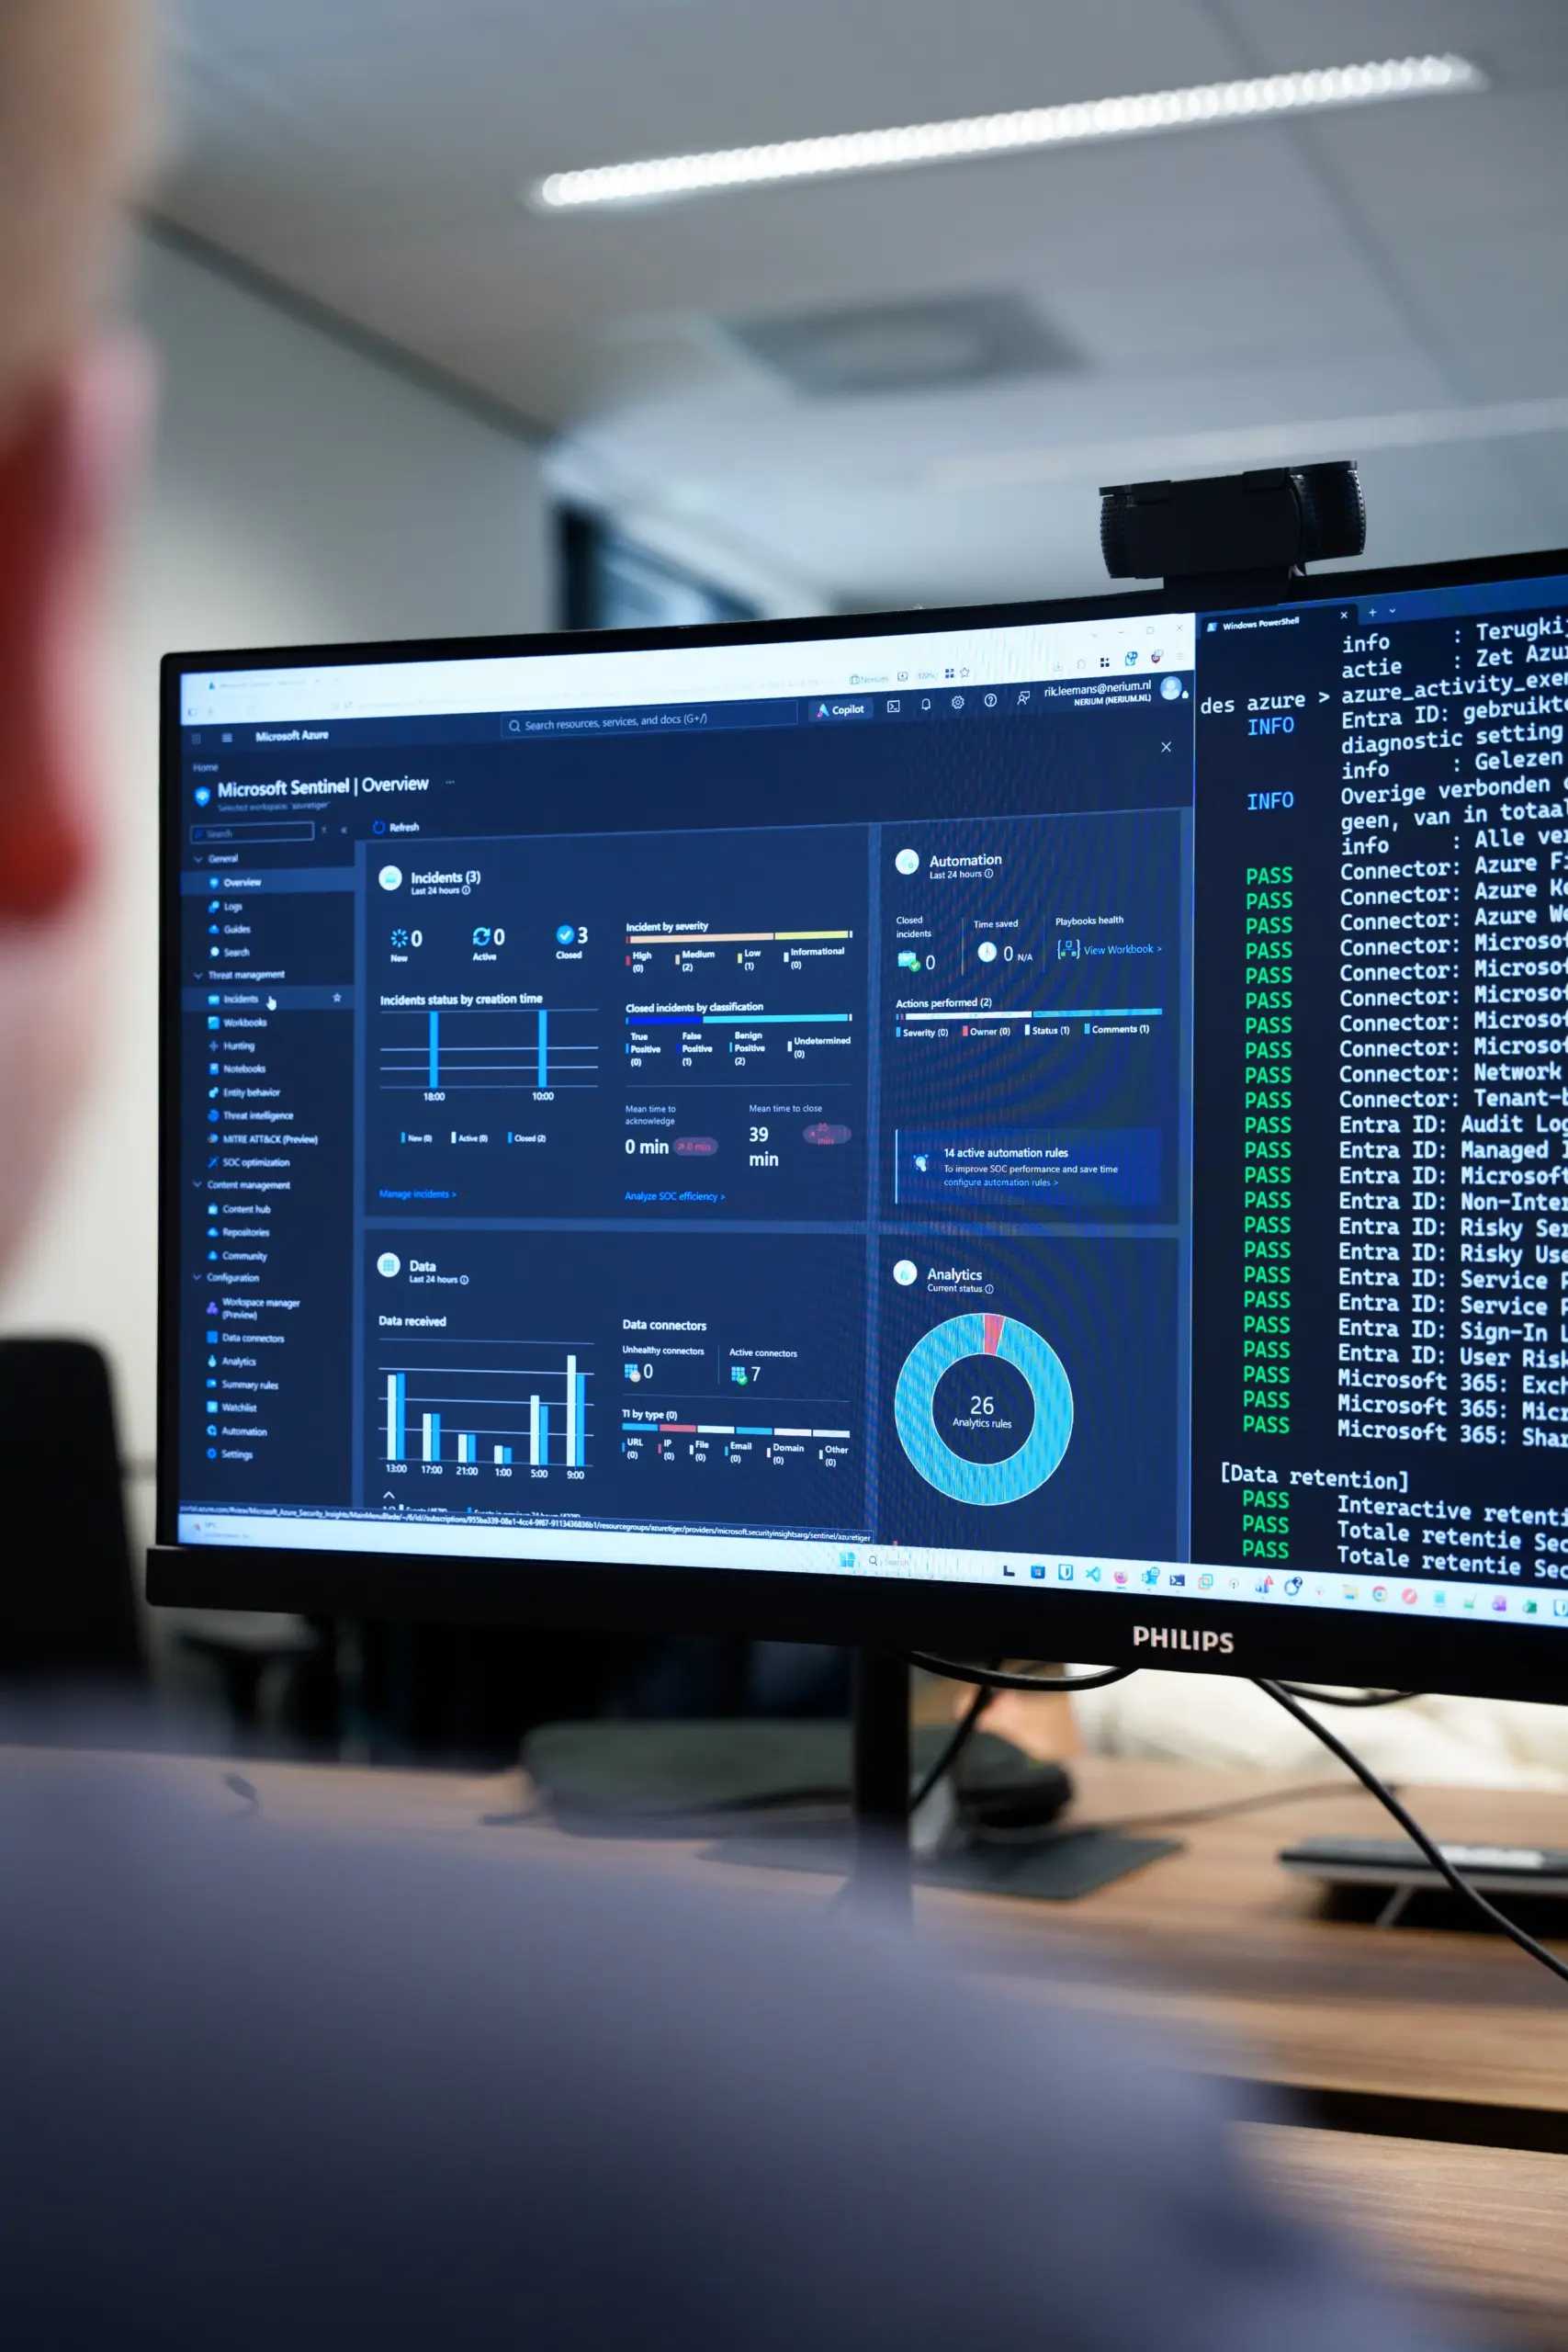
Do you have your own security team but need additional expertise or capacity? With Nerium’s hybrid SOC (Security Operations Center), your specialists and our security experts work as one team. We divide responsibilities and work together to strengthen monitoring, detection, and response.

  • 24/7 protection
  • Maintain Control
  • One Dutch team
Hybrid SOC. Your security team. Nerium as an extension.

“Nerium understands what we need and implements solutions that truly meet those needs.”

“Nerium understands what we need and implements solutions that truly meet those needs.”

“Nerium understands what we need and implements solutions that truly meet those needs.”

Two teams. One Security Operations Center.

Two teams. One Security Operations Center.

Not every organization wants to fully outsource its security operations. Perhaps your organization already has an experienced security team, but lacks the capacity for 24/7 SOC monitoring, specialized detection engineering, or the handling of major cyber incidents.


With a hybrid SOC, you combine your organization’s knowledge with Nerium’s expertise and capacity. We work in the same environment, establish clear agreements, and strengthen what’s already in place.
Collaborate in a way that suits your organization.

No two organizations are alike. That’s why we tailor the division of labor to the knowledge, capabilities, and goals of your internal security team. How would you like to work together?

01. Additional SOC Monitoring

Your team handles security monitoring during business hours. Nerium takes over monitoring outside of those hours, ensuring that threats are tracked even in the evenings, at night, and on weekends.

02. Specialized Support

Your team handles daily reports. Nerium provides support in the areas of detection engineering, automation, complex threats, and the response to major cyber incidents.

03. Growing Together

We share knowledge, improve detection methods, and support your team in further professional development. As internal capacity grows, responsibilities can be redistributed.

Clear agreements. Smooth collaboration.

An effective hybrid SOC requires more than just dividing up tasks. That is why we establish in advance who is responsible for what, how incidents are escalated, and when action is taken.

01. Understanding Your Organization

We assess the existing people, processes, technology, and risks. Together, we determine where Nerium adds the most value.

02. Defining Roles and Responsibilities

We agree on who will review reports, make decisions, and is authorized to take action. We also clearly define escalation procedures and responsibilities.

03. Working Together as One Team

Both teams work in the same environment and with shared information. Regular handoffs, short lines of communication, and clear points of contact ensure continuity.

04. Continuing to Improve Together

We evaluate incidents, detections, and collaboration. Through regular consultations, knowledge sharing, and joint exercises, the SOC continues to align with your organization.

One Dutch security team

You’ll work with a dedicated team of Dutch-speaking specialists who are familiar with your environment—from SOC analysts and detection engineers to experienced incident responders.

Flexible and independent

The partnership grows alongside your organization. Data, configurations, and customer-specific detections remain in your own environment and under your control.

Senior expertise at your fingertips

Experienced specialists are also involved in day-to-day security operations. This allows your team to immediately discuss complex threats
and incidents.

Scale Up Immediately in the Event of Incidents

In the event of a serious cyber incident, you’ll immediately contact our Incident Response specialists. The Incident Response Retainer is part of our partnership.

Stronger Together in Detection and Response.

Stronger Together in Detection and Response.

A hybrid SOC is a collaborative model within our core Managed Detection & Response (MDR) service. We combine the expertise of your internal team with our 24/7 monitoring, specialized Detection Engineering, and experience with complex cyber threats.


In the event of major incidents, our Incident Response specialists can provide immediate support. Thanks to pre-established agreements and our knowledge of your environment, it quickly becomes clear who is responsible for which actions.

A partnership that works in practice.

Discover how Nerium partners with organizations to strengthen security teams, identify threats, and address cyber incidents in a targeted manner.

Cta image

Want to strengthen your existing SOC?

Together, we’ll determine how Nerium can best complement your security team. 
With the right expertise, capacity, and a division of responsibilities that grows along with your organization.

Request a no-obligation consultation