Detection Engineering. Detect what standard security misses.

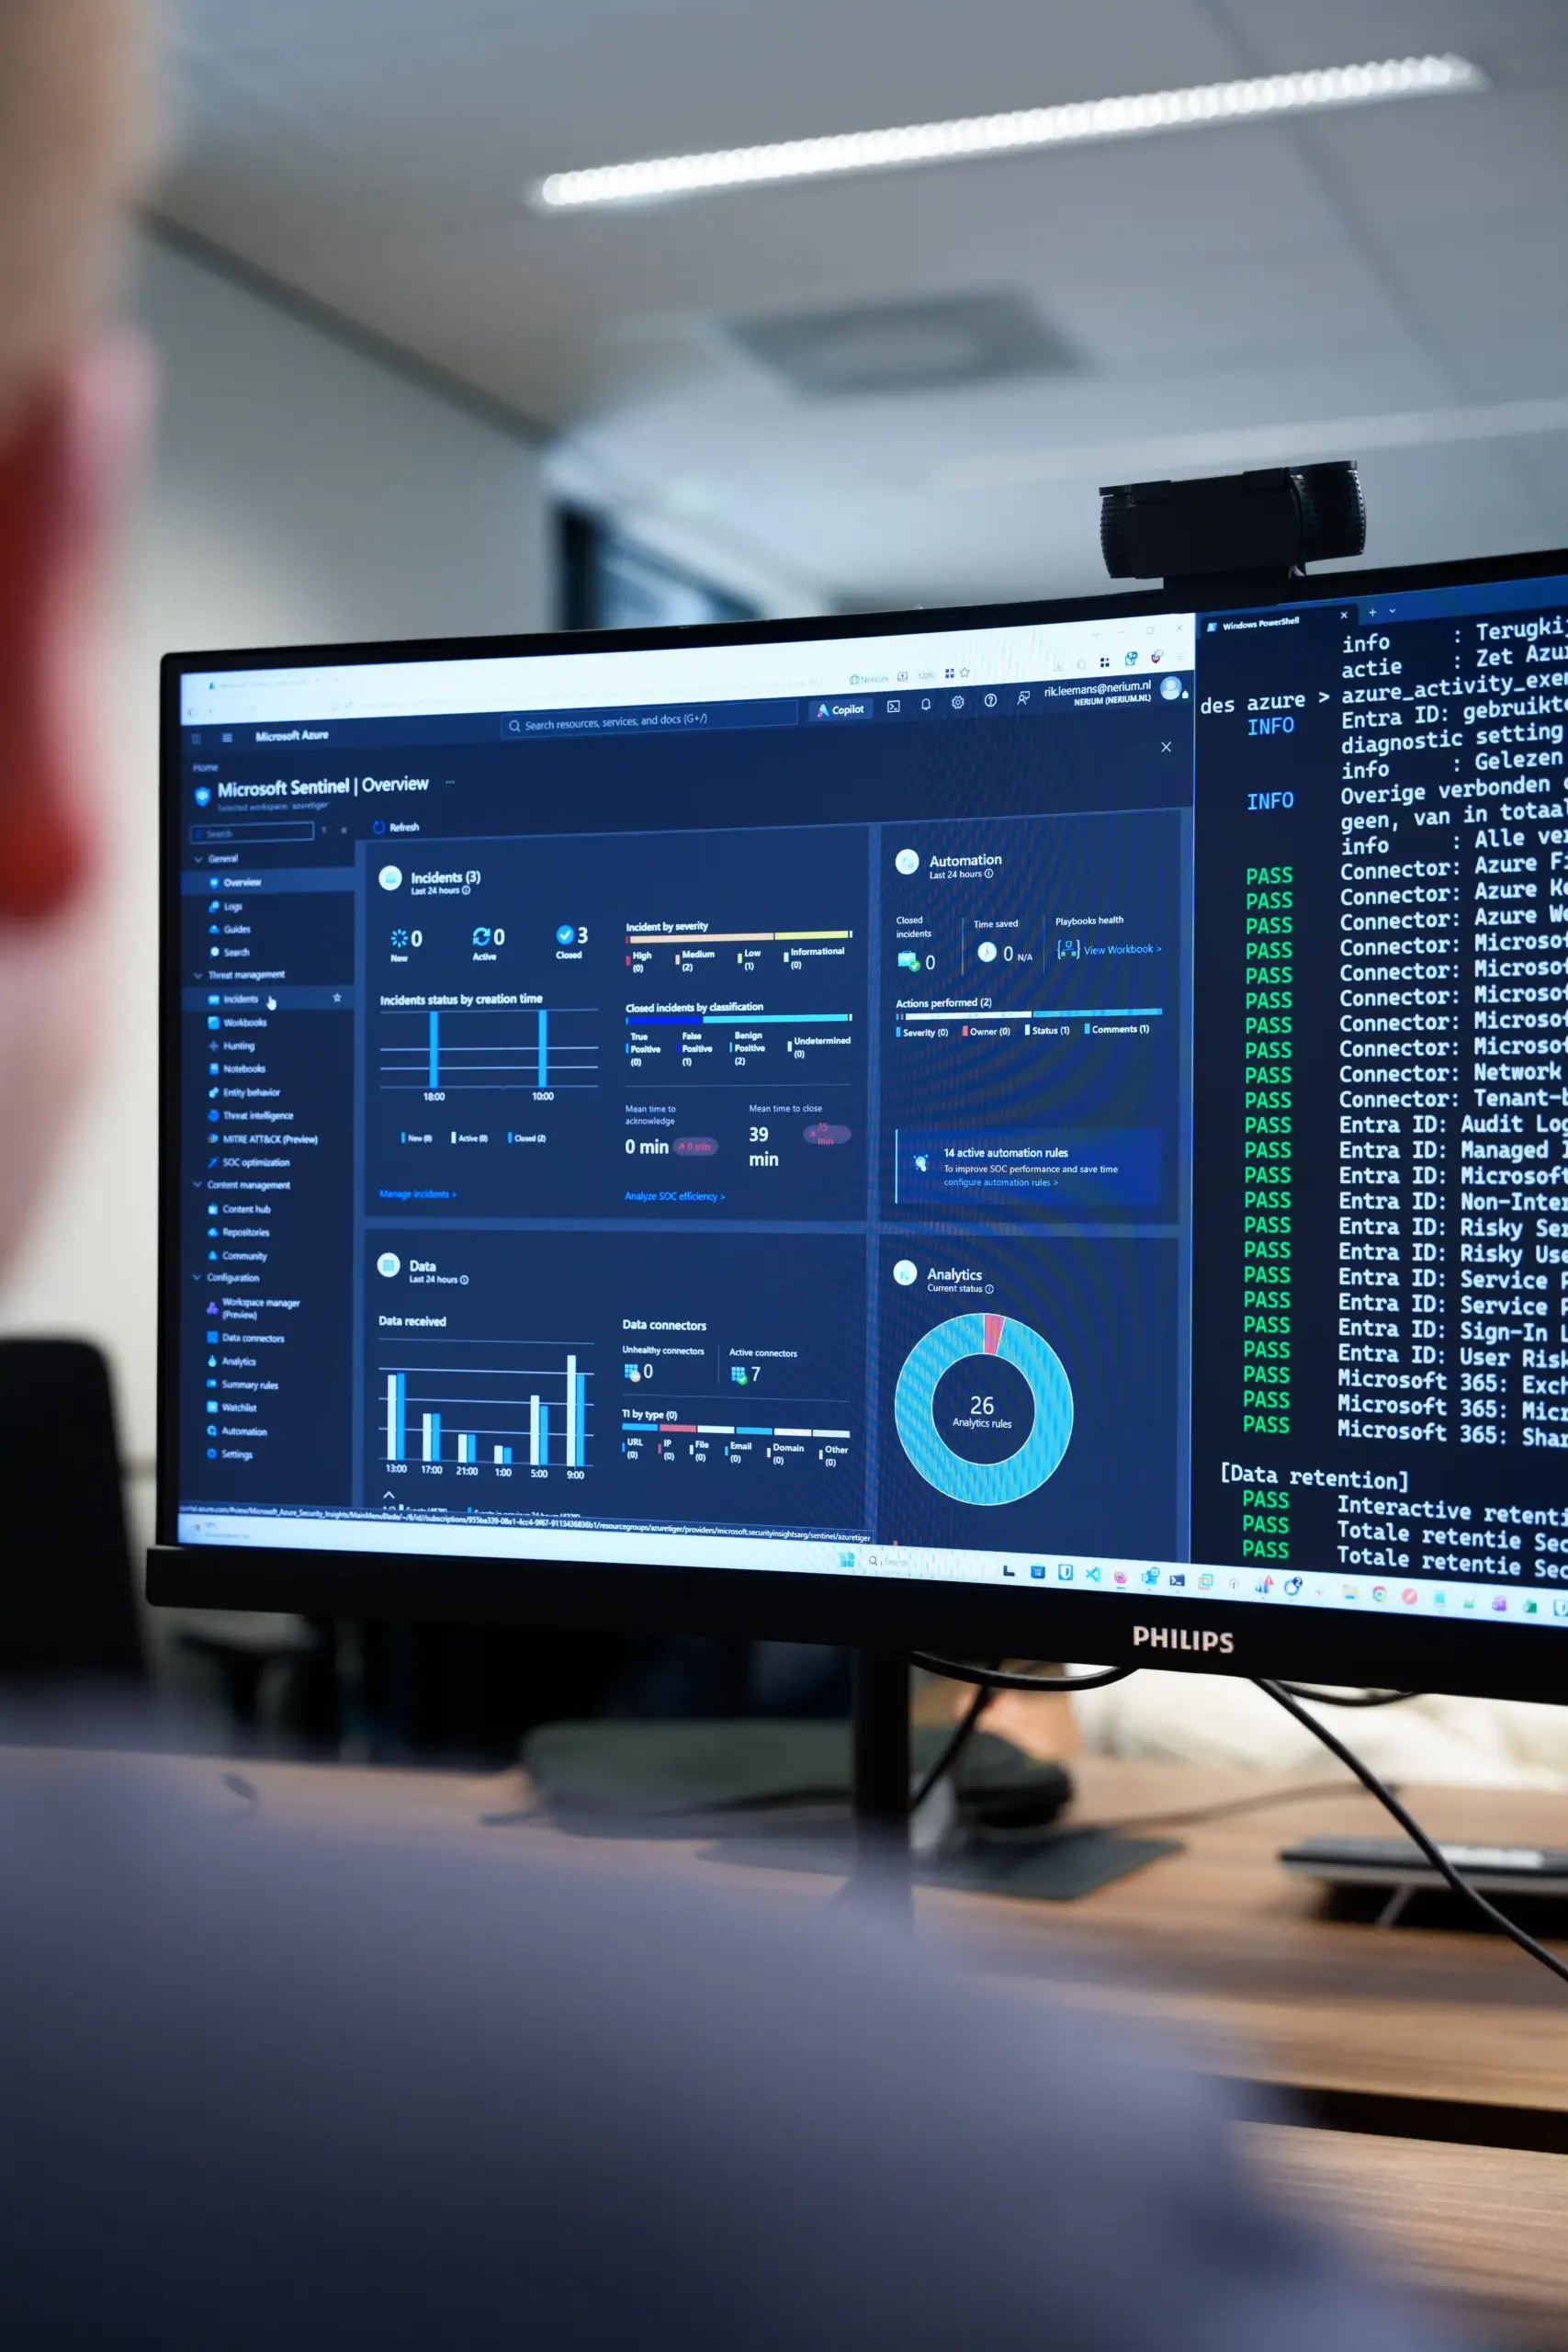
Standard security solutions do not detect every cyber threat. With Detection Engineering, Nerium develops detection rules tailored to your IT environment. Our specialists continuously test and refine these, supported by Detection-as-Code and our own technology.

  • 150+ self-detections
  • Detection-as-Code
  • Continuous optimisation
Detection Engineering. Detect what standard security misses.

“Thanks to Nerium’s specialist knowledge, we can continue to focus on providing high-quality and safe care for our clients.”

“Not a traditional supplier, but a dedicated security partner based in the Eindhoven region. Communication is straightforward and they know our organisation well.”

“Whether it’s a minor report or a serious incident, we know that Nerium is there for us 24/7.”

“Greater control over our digital security, specialist knowledge and prompt follow-up. That gives us confidence and peace of mind.”

“Specialist knowledge is not a luxury for our sector, but a necessity. Nerium’s targeted approach is convincing.”

“With Nerium as our partner, I sleep a lot more soundly. Their expertise and 24/7 protection give us peace of mind.”

“With Nerium, we’ve got our digital security well organised, without having to do everything ourselves. It’s exactly the support we need.”

Standard detection doesn’t catch everything. We go one step further.

Standard detection doesn’t catch everything. We go one step further.

Security solutions such as Microsoft Defender and CrowdStrike form an important foundation for cyber detection, but they are not familiar with your specific IT environment. As a result, suspicious activities may go undetected, such as the misuse of administrative privileges, compromised accounts or attacks via bespoke applications and external links.


Nerium addresses these blind spots with its own detection rules. These are based on realistic attack techniques and tailored to the risks and business processes that are important to your organisation.

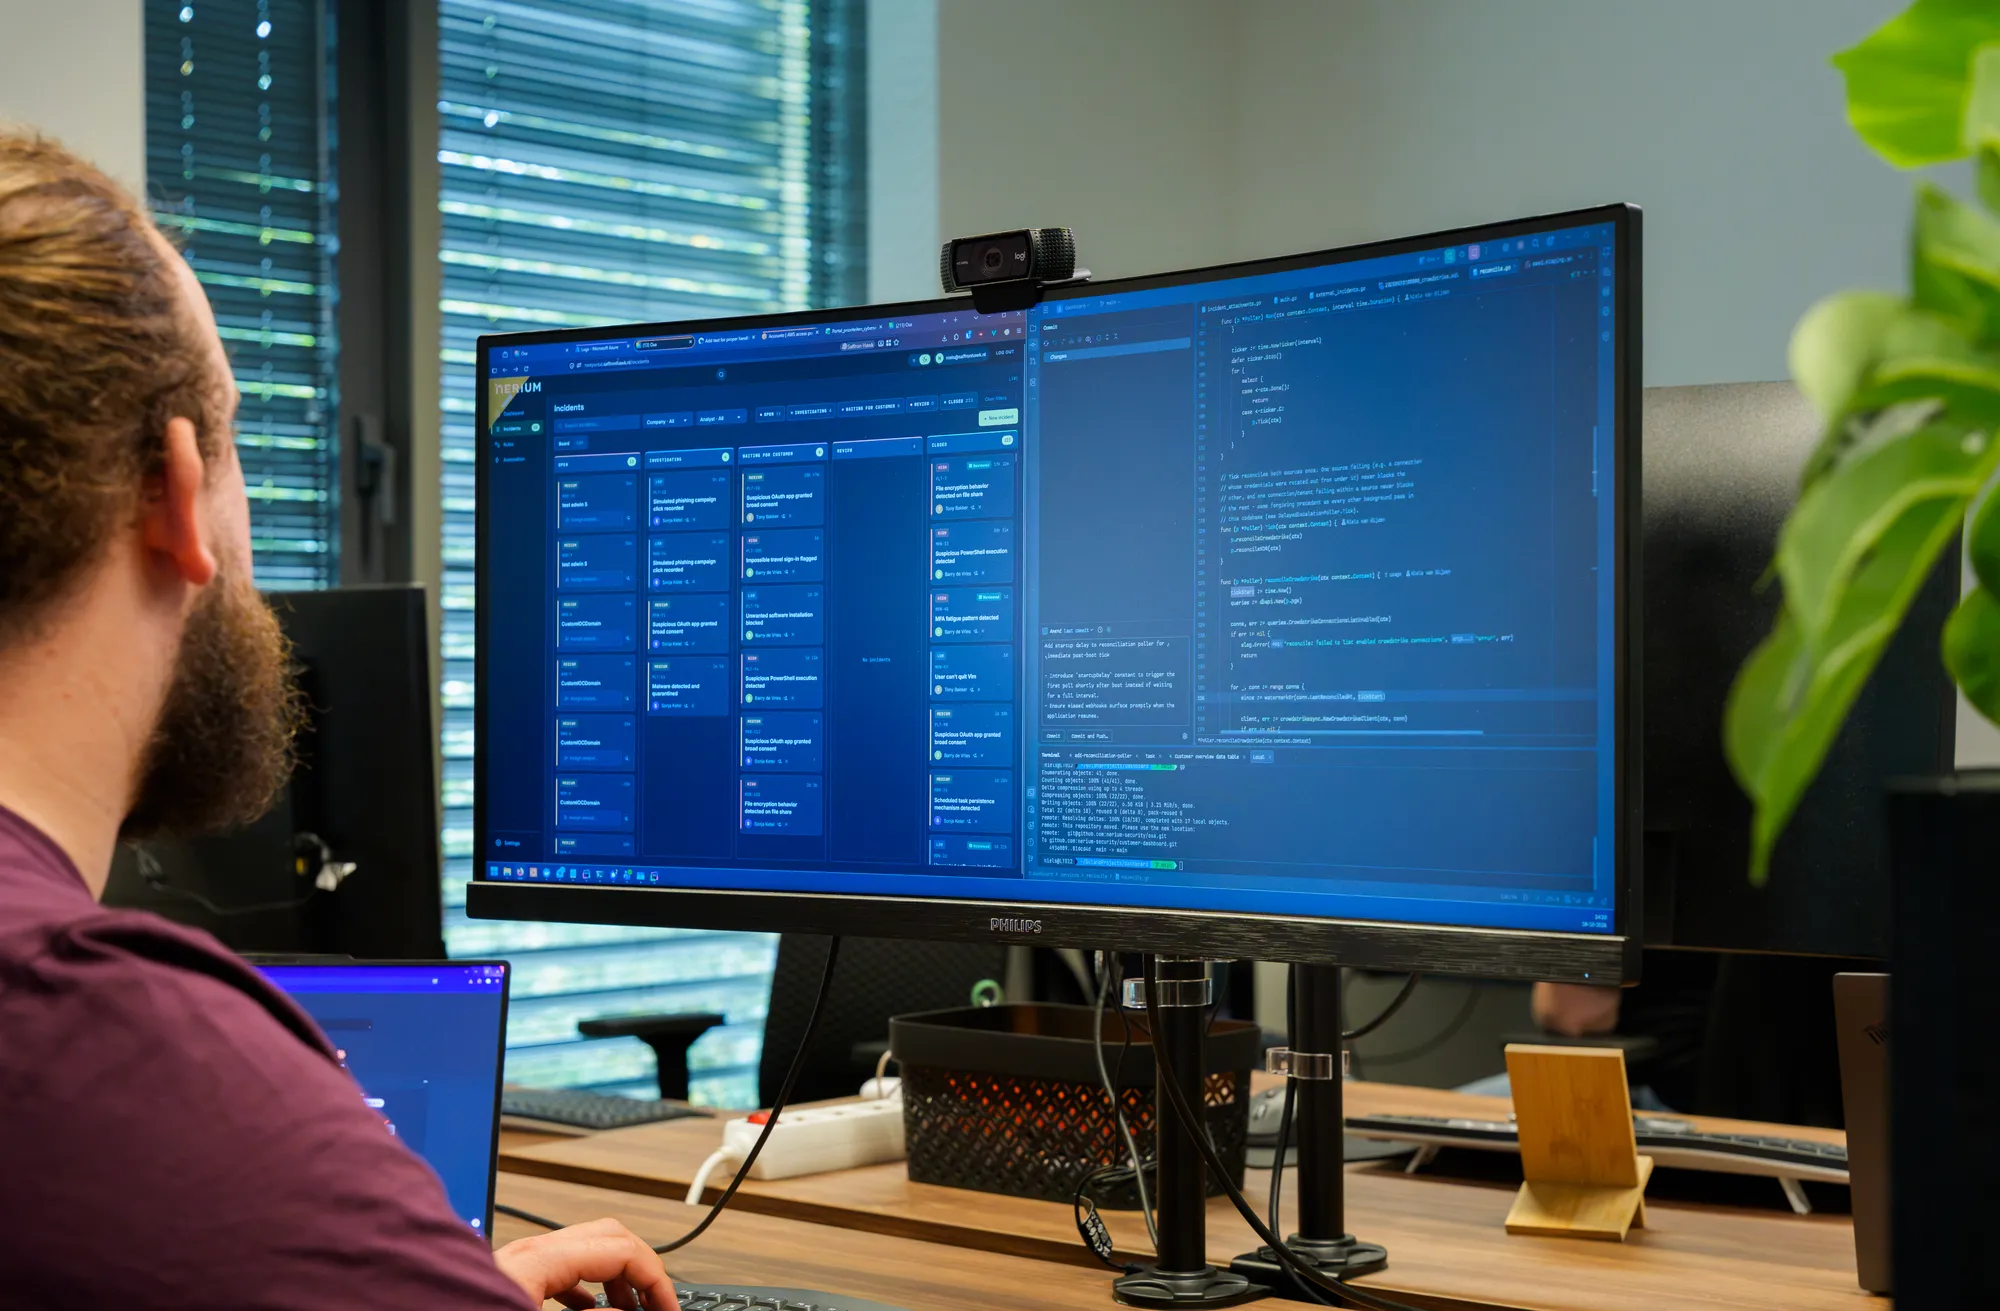
Multi-layered detection. Tailored to your organisation.

Standard detection methods provide an important foundation, but do not always address the specific risks faced by your organisation. Nerium therefore develops its own detection rules that look beyond any single system or supplier.

150+ in-house detection use cases

Our own library containing over 150 detection use cases, developed by our detection engineers based on practical experience and current threats.

Looking beyond a single supplier

We combine relevant data from endpoints, identities, cloud environments, network traffic and additional log sources.

Tailored to your IT environment

We combine generic detections with customer-specific context to identify suspicious activity more accurately and minimise unnecessary alerts.

Continuously tested and improved

We assess detections on a weekly basis in terms of performance, false positives and coverage, and adjust them in line with new threats or changes to your IT environment.

15 min. from detection to isolation

15 min. from detection to isolation

During a red team exercise at Almere City Council, Nerium’s proprietary detection rules identified an attack and the affected workstations were isolated within 15 minutes.

Real-life example; no guaranteed response time.

From Attack Scenario to Effective Detection

Effective Detection Engineering starts with understanding potential attacks. Using Threat Modeling, up-to-date threat intelligence, and experience from Incident Response, we determine which detection capabilities your organization actually needs.

01. Identifying Attack Scenarios

We are investigating realistic attack vectors and blind spots. Using MITRE ATT&CK, we determine which attack techniques are already being detected and where additional coverage is required.

02. Developing Detection Rules

We identify the traces attackers leave behind and determine which log sources are required. We then develop detection rules tailored to your IT environment.

03. Testing and Implementation

We test new detection rules against historical data and implement them in a controlled manner using Detection-as-Code, including documentation and response protocols.

04. Monitoring and Optimization

We continuously monitor whether detections are still working, minimise false positives and adapt rules in line with new attack techniques and evolving risks.

Smart automation. Fully transparent.

Nerium combines its own technology with human expertise to efficiently develop, manage and improve detection rules. Smart automation and clear insights give you greater control over the operation and coverage of your security.

Exine | Detection-as-Code

With Exine, we manage and implement detection rules as code. Thanks to automated processes, rules are rolled out in a controlled manner and configured with customer-specific settings.

Oxa | Understanding your detection

Via Oxa, Nerium’s own platform, you can see which detections are active, what they cover and how they are performing. This ensures you have a clear overview of how your security system is working.

Targeted detection. Stronger protection.

Targeted detection. Stronger protection.

Detection Engineering is a key component of our core
service Managed Detection & Response (MDR). By combining our own detection rules with 24/7 monitoring and Incident Response, we can not only identify threats but also follow them up in a targeted manner.


Threat Modelling helps to determine which attack scenarios are relevant to your organisation. We translate these insights into detection rules that align with your critical processes and systems.

Proven when it matters most.

Find out how Nerium helps organisations to detect cyber threats earlier, respond more effectively and continuously strengthen their digital resilience.

Cta image

Do you know what’s missing from your security?

Find out where your detection is falling short and how you can strengthen it in a targeted way. Nerium develops and refines detection rules that are tailored to your organisation and the threats that really matter.

Ask for advice, with no obligation